Independent security assurance and editable documentation to keep organizations secure, compliant and resilientQuestions? contact@rootguardsecurity.com
Whatever You Need to Prove, Start With It Written Down
Six complete, editable documentation sets, each mapped to the framework somebody is actually asking you about. Deploy one yourself, or have it rewritten against the systems you run. You own the files either way.
Customers send security questionnaires before they sign. Insurers ask for your policies before they quote. Auditors and boards want evidence rather than assurances. Writing all of that down correctly, and keeping it current as the rules change, is exactly the work most teams have no time to do well.
A pack is where that starts. It is not where it finishes, and the page says so further down rather than leaving you to discover it.
Build a Security Program
For an organization standing something up from nothing, or replacing a set nobody follows.
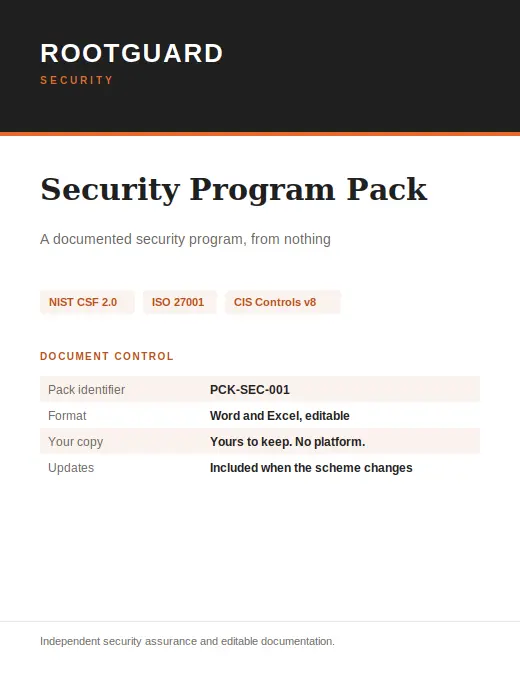
Security Program Pack
Stand up a documented security program from nothing, mapped to NIST CSF 2.0, ISO 27001 and CIS Controls, for when customers, insurers or investors ask.
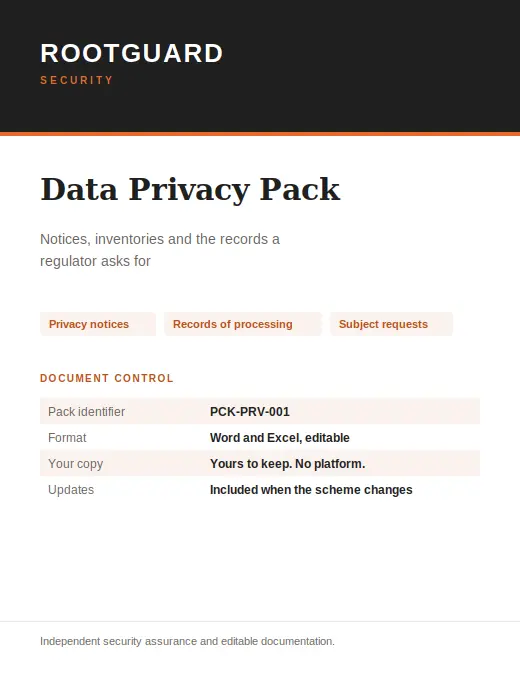
Privacy notices, data inventories, retention schedules, subject request workflows and the processing records a regulator or a customer will ask to see.
For the day something happens, and for the insurer who asks beforehand what you would do.
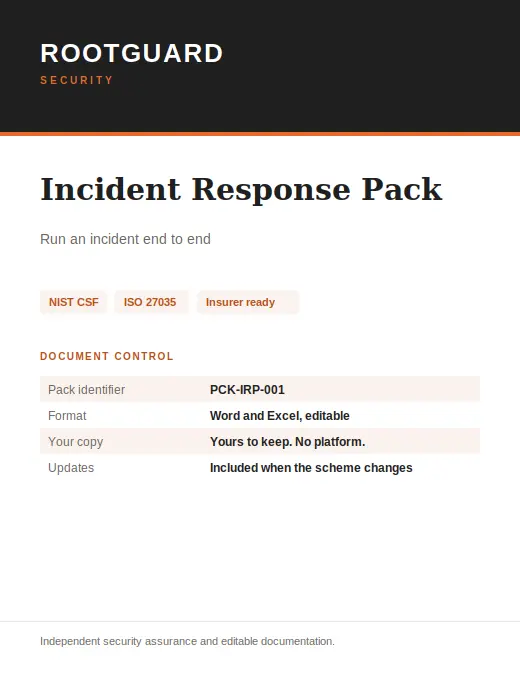
Incident Response Pack
Run an incident end to end: playbooks, evidence-collection procedures, severity criteria, and the templates to brief executives, regulators and insurers.
Documentation proves intent. Only an assessment proves the control behind it is operating. Knowing which rung you actually need is worth more than any pack on this page.
Each rung costs more than the one below it and proves something the one below it cannot.
1
The Pack
Complete editable documents with bracketed fields you resolve yourself.
Proves intent, if you do the work
2
Pack, Customized
One intake form. Every document rewritten against the systems you run and the obligations you carry.
Proves intent, correctly stated
3
Assessment
Every control tested against evidence, then documented, specified and verified.
Proves the control operates
4
Assurance
Verification on a cycle that what was agreed has genuinely closed, and what has drifted since.
Proves it still operates
Most organizations need rung one or two and are being sold rung three. If a customer asked for your policies, a pack answers them. If they asked for evidence that the policies are followed, it does not, and we would rather say that here than after you have bought one.
Three Things That Do Not Change
Built by Practitioners
Written and kept current by people who run security operations and sit real audits, not a documentation factory turning out generic sets.
Editable, and Yours to Keep
Word and Excel files you adapt to your business. No platform to log into, no subscription, no lock-in.
Buy Once, Updates Included
When the framework or the scheme changes, we send you the updated pack. The purchase keeps earning after you download it.
Nothing Here Fits? Commission a Pack
For a standard none of the six covers. Sector schemes, a parent company's own framework, or a contractual annex somebody has handed you.
What We Need From You
The standard or scheme, who is asking for it, and the deadline. If somebody sent you a document naming it, that is usually enough.
What We Come Back With
Scope, document count, a fee and a date, in writing, before anything is built. You decide from that rather than from an estimate.
What It Is Not
An assessment. A commissioned pack is documentation, and whether the controls it describes are operating is a separate engagement. We say so on the documents.
Not Sure Which PackAnswers the Question?
Tell us who is asking and what they asked for. We will name the pack, or tell you that a free download covers it, or that what you actually need is an assessment rather than a document set.